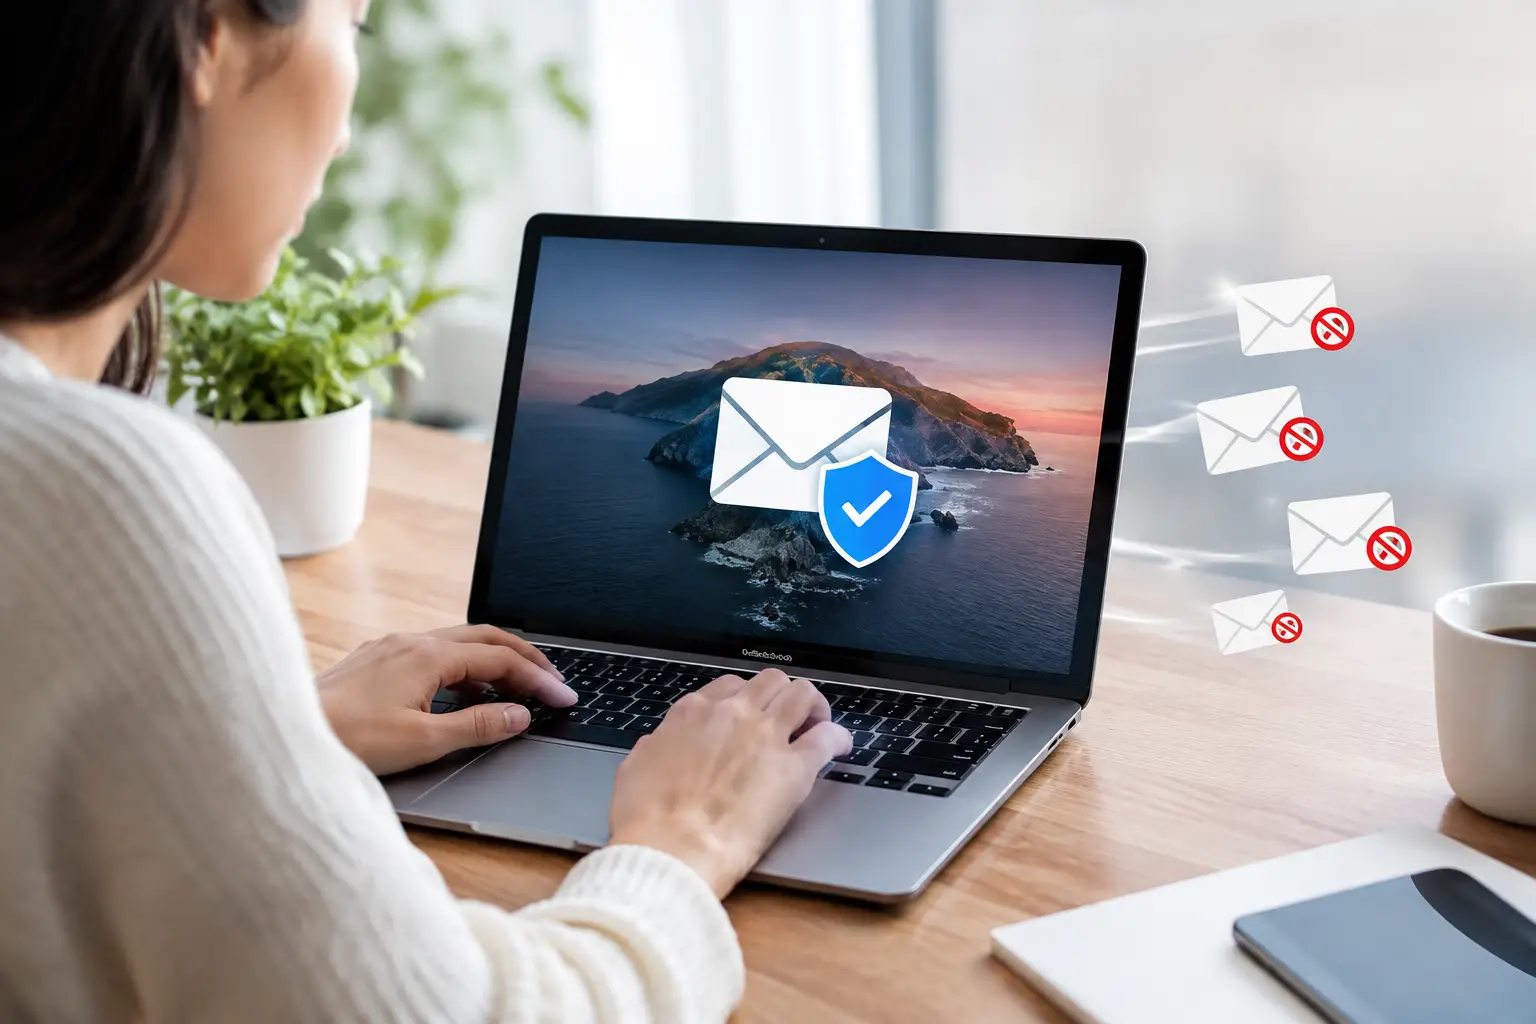
A convincing phishing message rarely arrives looking obviously dangerous. It may appear to be a delivery update, a Microsoft 365 warning, an Apple receipt or a message from a colleague asking you to review a document. The best way to block Mac phishing is not to rely on one setting alone, but to combine sensible Mac security, good email habits and a clear plan for what to do when something feels wrong.
For many households and small businesses, the real risk is not a hacker breaking into a Mac through a technical trick. It is being persuaded to hand over an Apple Account password, bank details or access to an email account. Once a criminal controls email, they can reset passwords for many other services too.
What Mac phishing looks like in real life
Phishing is an attempt to make you act quickly before you have time to check. The message may claim that your iCloud storage is full, your account will be closed today, or that an invoice needs urgent payment. A fake website can look remarkably like Apple, your bank, a courier or a familiar supplier.
On a Mac, phishing can also arrive as a browser pop-up. It might announce that your computer is infected and urge you to ring a number, install a cleaner or allow remote access. Apple does not put a phone number in a sudden Safari warning and ask you to call for support. Treat this as a scam, even if the message uses an Apple logo or makes alarming noises.
Small businesses are often targeted with messages that seem to come from a director, bookkeeper, customer or delivery firm. An email address can look close enough to the real one to pass a quick glance. A request to change bank details, buy gift cards or sign in to view a shared file deserves a second check, preferably by phoning the person on a trusted number rather than replying to the email.
Start with the protections already on your Mac
Your Mac includes useful security features, but they need to be kept up to date. Install macOS updates promptly, especially security updates. Open System Settings, choose General, then Software Update, and turn on automatic updates if that suits the way you work. If you use an older Mac that cannot run the latest macOS, it is worth getting advice on the safest options rather than assuming it is still fully protected.
Safari helps identify fraudulent websites. In Safari, open Settings, select Security and make sure the option to warn when visiting a fraudulent website is enabled. This will not catch every new scam, but it is a worthwhile layer of protection.
Keep the built-in firewall switched on as well. In System Settings, go to Network and then Firewall. The firewall is not a phishing filter, but it helps control unwanted incoming connections to your Mac. It is one part of good general housekeeping.
Use a separate, standard user account for everyday work if you are comfortable doing so, particularly on a shared family Mac. An administrator account has more power to install software and change settings. That extra step can reduce the chance of a rushed click making a bigger mess.
Use Mail filters carefully, not blindly
Apple Mail and most email providers already identify a great deal of junk and phishing. When an obvious scam reaches your inbox, select it and use the Junk option. This helps Mail learn what you do not want. If it is pretending to be from a genuine organisation, use any reporting option offered by your email provider too.
Be cautious with rules that automatically delete messages based on a few words. Fraudsters constantly change their wording, while legitimate emails can contain words such as “invoice”, “payment” or “security”. An overzealous rule could hide a real customer enquiry or an important account notice.
For a home user, sensible junk filtering plus regular checks of the Junk folder is usually enough. For a business using Microsoft 365 or Google Workspace, stronger filtering, domain protection and staff awareness can make a meaningful difference. The right setup depends on how much genuine email you receive, whether staff share addresses and how costly it would be to miss a real message.
The checks that stop most phishing attempts
Before clicking a link, pause and look at the sender’s full email address, not just the display name. A message that says it is from Apple but comes from an unrelated address is not genuine. Be alert for subtle misspellings, extra words or swapped letters in web addresses.
If you hover the pointer over a link in Mail, Safari will usually show where it leads. On a trackpad, do not click while checking it. If the address looks unfamiliar or does not match the organisation named in the message, leave it alone.
It is safer to open a new browser window and visit the service yourself, or use its official app. For example, if a message says there is a problem with your Apple Account, go to Apple’s account settings directly rather than using the email link. The same approach works for banks, couriers, HMRC and suppliers.
Never enter a password after following an unexpected link. A genuine service may occasionally ask you to sign in, but you do not need to do so through a surprise email. That small change of habit removes much of the danger.
Passwords and two-factor authentication matter more than ever
A different, strong password for every important account limits the damage if one password is stolen. iCloud Keychain, now called Passwords on newer Apple systems, can create and save strong passwords for you. This is safer than reusing a memorable password with a number or exclamation mark added to the end.
Turn on two-factor authentication for your Apple Account, primary email account, banking and business services. It means a stolen password alone is less likely to be enough for someone to get in. Avoid sharing verification codes with anybody, even if they claim to be from Apple, your bank or IT support. A legitimate support provider will not need your one-time security code.
For businesses, consider who has access to shared inboxes, website logins and payment systems. A former employee’s old login or one shared password written in a notebook can undo otherwise good security. Review access when roles change, and use individual logins wherever possible.
What to do if you clicked something
Clicking a suspicious link does not automatically mean your Mac is infected. If you did not enter information, download anything or allow a prompt, close the page and do not return to it. Clear Safari’s history if it helps you avoid reopening the page by mistake.
If you entered a password, change it immediately using the genuine website or app. Start with the affected account, then change any other account that used the same password. Check recent sign-ins, recovery details, forwarding rules in email and bank activity. Contact your bank straight away if you entered card or banking information.
If you downloaded an unknown app, allowed remote access or gave someone control of your Mac, disconnect from Wi-Fi or unplug the network cable if practical. Do not keep talking to the caller. A proper check can identify unwanted software, remove remote-management tools, review browser extensions and make sure your accounts are secure.
Do not let fake pop-ups take over Safari
Scam pop-ups are designed to create panic. If Safari appears stuck, press Command, Option and Escape together, select Safari and choose Force Quit. Reopen Safari while holding Shift to help prevent previously open pages loading again. You can then remove suspicious extensions in Safari Settings under Extensions.
Be wary of browser notifications too. Some websites persuade visitors to click “Allow” and then send fake virus alerts as notifications. In Safari Settings, review Websites and Notifications, then remove permissions for sites you do not recognise. If the problem persists, a careful review of your browser settings and installed software is sensible.
A calmer way to stay safe
The aim is not to make using your Mac stressful or to distrust every message. It is to build a short pause into the moments scammers rely on: unexpected urgency, a password request, a payment change or a frightening pop-up. Genuine organisations will still be there when you have checked through the proper route.
If a message, pop-up or login page has left you uncertain, stop before deleting evidence or changing lots of settings at random. A patient, hands-on check can be far less worrying than trying to work it out alone, particularly when family photos, business email or online banking are involved. North Dorset Mac Man can help Dorset Mac users review what happened, secure accounts and put practical protections in place for next time.